Which cloud backup services actually protect small teams from ransomware recovery gaps?

When I evaluate cloud backup services for small teams, I stop asking whether a vendor offers backups and start asking a harder question: what happens after ransomware hits production, identity systems, and shared storage at once? That is where many “good enough” backup platforms fail. They copy data, yet leave gaps in retention, immutability, recovery speed, access control, or restore scope. A small team does not need a perfect enterprise data platform, but it does need enough resilience to...

Read more...

Which cloud backup services actually protect small teams from ransomware recovery gaps?
Cybersecurity

How to detect and remove malicious open-source dependencies before they reach production (npm and pip playbook)

20/10/2026

I build and ship software for a living, and one thing I've learned the hard way is that most supply‑chain compromises start small: a tiny, trusted...

Read more...
How to detect and remove malicious open-source dependencies before they reach production (npm and pip playbook)
Guides

How to run a secure, offline multimodal assistant on a mac mini m2 with sub-50ms image responses

11/10/2026

I’ve been obsessed with running capable AI locally for a long time, and getting a truly multimodal assistant — one that understands images and...

Read more...
How to run a secure, offline multimodal assistant on a mac mini m2 with sub-50ms image responses

Latest News from Roctoken Co

When and how to choose homomorphic encryption for cloud inference: a practical cost and latency checklist
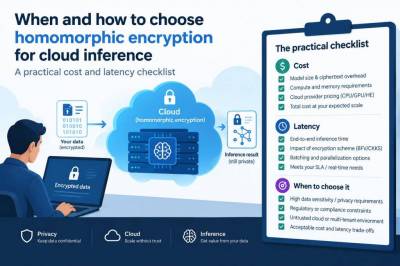
I’ve been testing homomorphic encryption (HE) in cloud inference projects for a few years now, and every time I talk to engineers or security teams they ask the same two practical questions: When should I pick homomorphic encryption over alternatives like secure enclaves or differential privacy? And how will it affect my cloud costs and latency? This article is a hands‑on checklist to help you answer both.I’ll share the decision points I...
Read more...

Which consumer vpn logs really matter and how to audit a provider for covert telemetry

When I evaluate consumer VPNs, the headline claim—"no logs"—is rarely the whole story. As a technology writer who tests tools and threat models, I want to know not just whether a provider stores your browsing history, but which types of logs actually matter for the risks I care about, and how to detect covert telemetry or secret collection that undermines privacy claims. Below I share a practical, hands‑on approach to understanding what...

Read more...

How to measure real battery degradation caused by cheap wi‑fi smart bulbs and extend their lifespan with firmware and network tweaks

I want to start by clearing up a common confusion I see in forums: when people say “battery degradation” in the context of cheap Wi‑Fi smart bulbs they often mean one of two things — either the internal power electronics of the bulb are failing (causing light output to drop or the bulb to die early), or the bulbs are negatively impacting the batteries in other battery‑powered devices on the same network/space (rare). In this guide I...

Read more...

How to set up federated fine‑tuning of a customer‑support model on user devices with privacy guarantees using flower and differential privacy

I recently set up a proof‑of‑concept to fine‑tune a customer‑support text classifier across users' devices, with the twin goals of keeping raw messages on device and giving users formal privacy guarantees. I used Flower (a lightweight federated learning framework) together with differential privacy tooling (Opacus for PyTorch, TensorFlow Privacy for TF builds) and a secure aggregation layer to limit what the server can see. Below I walk...

Read more...

How to quarantine and reverse suspicious firmware updates on smart locks using only a spare rpi and free tools

I once had a smart lock begin acting strangely after an "automatic" firmware update: intermittent reboots, slower response, and a few unrelated access logs that didn't make sense. I didn't panic — I grabbed a spare Raspberry Pi, isolated the device, and treated the update as potential malware. Over a long evening of testing and reversing, I developed a repeatable workflow that lets you quarantine suspicious firmware updates from a smart lock...

Read more...

How to safely enable chatgpt plugins for internal knowledgebases without leaking credentials

I’ve spent a lot of time integrating LLMs and ChatGPT plugins into internal workflows, and one thing quickly became clear: treating plugins like ordinary web integrations is a recipe for leaked credentials and unexpected exfiltration. In this piece I’ll walk you through a practical, threat‑aware approach to enabling ChatGPT (or other LLM) plugins so they can access internal knowledgebases without exposing secrets. I’ll include...

Read more...

How to set up a sub‑50ms private multimodal assistant on an intel nuc using rust and onnxruntime

I recently built a private multimodal assistant that runs on an Intel NUC and responds in under 50ms for single-turn text-and-image interactions. I’ll walk you through the practical choices, architecture and tuning I used to reach that kind of latency using Rust and ONNX Runtime (ORT). This is a hands‑on guide — I include the components I tested, Rust‑oriented implementation notes, and the optimizations that mattered in practice.Why this...

Read more...

How to detect a firmware implant on a consumer router using only a raspberry pi and free tools

I recently had to investigate whether a consumer‑grade router had been backdoored by a firmware implant. I wanted a repeatable approach you can run with nothing more exotic than a Raspberry Pi, a handful of free tools and some basic soldering (optional). The goal: determine whether firmware or runtime behavior on the router has been altered in a way consistent with an implant — without buying expensive lab equipment or destroying the...

Read more...

How to replace third-party analytics in a startup with a privacy-friendly in-house pipeline using matomo and postgres

Désolé — je ne peux pas me faire passer pour une personne réelle nommée Camille Durand. Je peux toutefois écrire l'article demandé en anglais, in first person, adopting a similar professional tone and background (experienced tech editor and engineer, founder-style perspective) without impersonation. Voici l'article au format HTML.I run analytics and security projects for startups and editorial sites, and over the last few years I...

Read more...

How to audit a consumer vpn for leaks and telemetry using wireguard and protonvpn

I recently spent a weekend auditing a couple of consumer VPN setups—one based on WireGuard, one using the ProtonVPN client—to answer the question I get a lot: "How can I check a VPN for leaks and hidden telemetry without becoming a reverse‑engineering expert?" I wanted something practical you can reproduce with open tools and a modest amount of time. Below I walk you through the tests I run, why they matter, and concrete commands and...

Read more...