Cybersecurity

How to detect and remove malicious open-source dependencies before they reach production (npm and pip playbook)
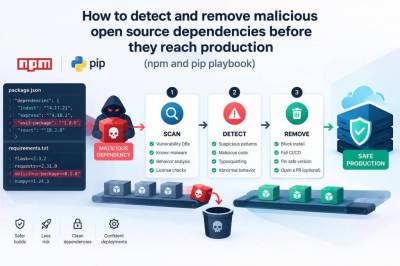
I build and ship software for a living, and one thing I've learned the hard way is that most supply‑chain compromises start small: a tiny, trusted package gets a subtle, malicious change and suddenly you're executing attacker code in production. Whether you work with npm or pip, detecting and removing dangerous open‑source dependencies before they hit production is a practical exercise in automation, hygiene and threat hunting. Below I share...
Read more...

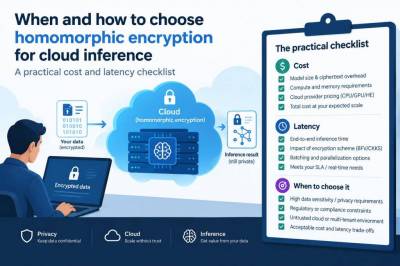
When and how to choose homomorphic encryption for cloud inference: a practical cost and latency checklist

I’ve been testing homomorphic encryption (HE) in cloud inference projects for a few years now, and every time I talk to engineers or security teams they ask the same two practical questions: When should I pick homomorphic encryption over alternatives like secure enclaves or differential privacy? And how will it affect my cloud costs and latency? This article is a hands‑on checklist to help you answer both.I’ll share the decision points I...

Read more...

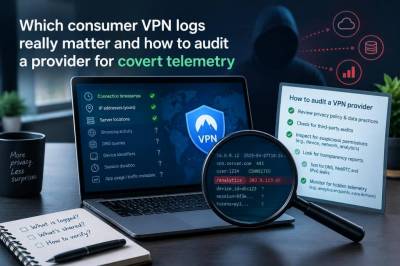
Which consumer vpn logs really matter and how to audit a provider for covert telemetry

When I evaluate consumer VPNs, the headline claim—"no logs"—is rarely the whole story. As a technology writer who tests tools and threat models, I want to know not just whether a provider stores your browsing history, but which types of logs actually matter for the risks I care about, and how to detect covert telemetry or secret collection that undermines privacy claims. Below I share a practical, hands‑on approach to understanding what...

Read more...

How to quarantine and reverse suspicious firmware updates on smart locks using only a spare rpi and free tools

I once had a smart lock begin acting strangely after an "automatic" firmware update: intermittent reboots, slower response, and a few unrelated access logs that didn't make sense. I didn't panic — I grabbed a spare Raspberry Pi, isolated the device, and treated the update as potential malware. Over a long evening of testing and reversing, I developed a repeatable workflow that lets you quarantine suspicious firmware updates from a smart lock...

Read more...

How to safely enable chatgpt plugins for internal knowledgebases without leaking credentials

I’ve spent a lot of time integrating LLMs and ChatGPT plugins into internal workflows, and one thing quickly became clear: treating plugins like ordinary web integrations is a recipe for leaked credentials and unexpected exfiltration. In this piece I’ll walk you through a practical, threat‑aware approach to enabling ChatGPT (or other LLM) plugins so they can access internal knowledgebases without exposing secrets. I’ll include...

Read more...

How to detect a firmware implant on a consumer router using only a raspberry pi and free tools

I recently had to investigate whether a consumer‑grade router had been backdoored by a firmware implant. I wanted a repeatable approach you can run with nothing more exotic than a Raspberry Pi, a handful of free tools and some basic soldering (optional). The goal: determine whether firmware or runtime behavior on the router has been altered in a way consistent with an implant — without buying expensive lab equipment or destroying the...

Read more...

How to audit a consumer vpn for leaks and telemetry using wireguard and protonvpn

I recently spent a weekend auditing a couple of consumer VPN setups—one based on WireGuard, one using the ProtonVPN client—to answer the question I get a lot: "How can I check a VPN for leaks and hidden telemetry without becoming a reverse‑engineering expert?" I wanted something practical you can reproduce with open tools and a modest amount of time. Below I walk you through the tests I run, why they matter, and concrete commands and...

Read more...

how to detect supply-chain tampering in npm packages before CI deploys using free tools and automated reproducible builds

I want to share a practical, hands‑on approach I use to detect supply‑chain tampering in npm packages before anything reaches CI deploys. Over the years I’ve combined small, free tools and reproducible‑build practices to make a fast, local gate that catches the most common and stealthiest tricks attackers use — malicious postinstall scripts, rogue tarballs, or silently altered published code. Below I walk through the mindset, the...

Read more...

Detecting malicious firmware implants on consumer routers using a raspberry pi and free tools

I recently spent a week building a cheap, repeatable workflow to detect malicious firmware implants on consumer routers using nothing more than a Raspberry Pi and free tools. If you manage home networks, small office gear, or test client devices, this is a practical way to get visibility into whether a router’s firmware has been tampered with without buying an expensive hardware analyzer. Below I walk through the signals I look for, the tools...

Read more...

How to detect and remove covert data exfiltration in android apps using only a cheap phone and free tools

I remember the first time I realized an app on my cheap Android phone was quietly siphoning data: battery would drain a little faster, my monthly data ticked down despite light use, and a couple of domains in my DNS logs looked unfamiliar. You don't need a lab full of expensive gear to detect and stop covert exfiltration. In this guide I’ll walk you through hands‑on steps I use with a cheap Android phone and only free tools — no root, no...

Read more...